NiKaDa NiKaDa
Home Our Model Pricing About Contact
NiKaDa Autonomous Cyber-Shield eBPF Hardware Architecture
01 // Systems Architecture & Telemetry Pipeline

5-Tier Rust eBPF &
Autonomous SOC Architecture

On-host 0.051 ms P50 (<0.08 ms SLA) L0 filtering, 0.131 ms P50 (<5 ms SLA) Tier-0 process micro-freeze, 14.35 ms P50 BETH eBPF DualEngine ML (99.74% accuracy), 5-Agent Local 33B/50B AI Swarm, and 0.054 ms P50 Ed25519 signed remediation.

Five Pillars of Defense

Fast-Lane Hot-Patching & 5-Tier EDR

Legacy tools only alert after a breach. CyberAI Shield v2.0 patches vulnerable runtimes at boot and freezes threats in sub-milliseconds.

Fast-Lane Zero-Day Hot-Patching
01

Fast-Lane Hot-Patching

Scans Linux & Windows at boot for PHP2Shell (CVE-2026-109618 & 109619), writes 99-cyberai-shield-php2shell.ini, reloads PHP with zero downtime, and emits EXECUTED_ACK.
Zero-Downtime · EXECUTED_ACK
Tier-0 Rust Micro-Freeze
02

Tier-0 Rust Micro-Freeze

Native Rust endpoint sensor (Linux & Windows) freezes ransomware, Mimikatz, and reverse shells via SIGSTOP / NtSuspendProcess in under 5 ms.

< 5 ms On-Host Response
5-Agent Autonomous AI SOC Swarm
03

5-Agent AI SOC Swarm

Combines 0.42ms IsolationForest + Redis Lua risk scoring with 5 specialized AI agents powered by locally trained 33B & 50B parameter security models.

Local 33B & 50B Models
Ed25519 Signed Remediation and Mirage PQC
04

Ed25519 & QuantumGuard

Verifies every KILL_PROCESS & ISOLATE_NETWORK directive with Ed25519 + composite PID (process_start_time_ns), Mirage honey-canaries, and PQC CBOM auditing.

0.054 ms P50 Ed25519 · NIST PQC
05

Sovereign India & 🇦🇺 Australia / NZ On-Shore Pods

Dedicated on-shore control planes with automated 6-hour CERT-In dossiers, 180-day tamper-evident retention, DPDP Act 2023 sovereignty, and Australian ACSC Essential Eight / APRA CPS 234 / SOCI Act compliance (including a Free 30-Day Trial with $0 setup fee for ANZ enterprises).

India Sovereign Pod · 🇦🇺 Free 30-Day ANZ Trial
Sub-Millisecond Precision

Kernel telemetry that freezes threats before encryption begins

Our Rust eBPF (Linux) and ETW (Windows) sensors operate at 0.08 ms L0 deterministic filtering SLA (0.051 ms P50 live measured) and <5 ms Tier-0 process suspension SLA (0.131 ms P50 / 0.191 ms P95 live measured)—stopping shadow-copy deletion, credential dumping, and web-shell spawns automatically.

  • 0.051 ms P50 (0.08 ms SLA) L0 Signature & Mirage Canary Filter
  • 0.131 ms P50 (< 5 ms SLA) SIGSTOP / NtSuspendProcess Freeze
  • 0.42 ms / 14.35 ms P50 Redis Lua + BETH eBPF Dual-Engine ML
  • Cryptographically Signed Verified Linux & Windows Sensors
Rust eBPF and ETW Kernel Micro-Freeze Visualization
Tier-0 Rust Sensor · Linux eBPF & Windows ETW 0.131 ms P50 Freeze (< 5 ms SLA)
Autonomous Judgement

Five specialized AI agents working in consensus

ForensicAnalyst, NetworkHunter, ThreatIntel, ResponseCoordinator, and ContainmentEngine correlate multi-step campaigns using sovereign-hosted, domain-fine-tuned 33B & 50B parameter security models—with zero third-party LLM API calls or external cloud data leakage.

Request 60-Second Deployment
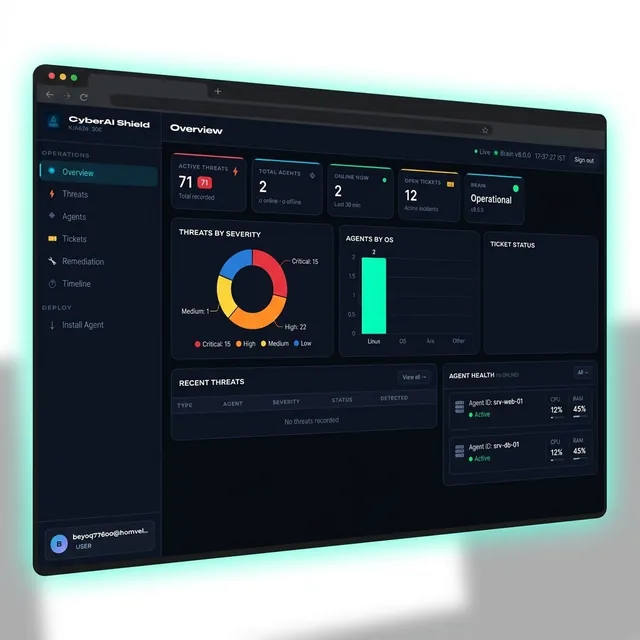
NiKaDa CyberAI Shield v2.0 SOC Control Plane Dashboard
CyberAI Shield v2.0 · Unified SOC Control Plane 5-Agent Swarm
Enterprise Architecture & Benchmark Disclosure

Verifiable specifications & shared responsibility

Designed for CISO, CTO, and security architecture due diligence: transparent measurement boundaries, sensor resource ceilings, AI model provenance, and regulatory control alignment. View full Benchmark Evidence Library →

01 · Latency & Containment Methodology

On-Host Ring-Buffer vs. Asynchronous Swarm Verdict

  • 0.051 ms P50 (0.08 ms SLA) On-host L0 in-memory signature & Mirage canary lookup across all 13 rules via BPF_MAP_TYPE_RINGBUF / Windows ETW (zero network round-trip).
  • 0.131 ms P50 / 0.191 ms P95 (< 5 ms SLA) Tier-0 on-host process thread suspension (SIGSTOP / NtSuspendProcess) measured via CLOCK_MONOTONIC_RAW across 50 real OS processes.
  • 0.42 ms Redis Lua + 14.35 ms P50 ML Control-plane Layer-1 atomic Redis 7.4 Lua risk decay + 16-feature CyberAI_Shield_eBPF_DualEngine_v1 (XGBoost + IsolationForest, 99.74% accuracy).
  • Asynchronous L2 Verdict (0.054 ms Sign) 5-Agent 33B/50B Swarm forensic consensus dispatches RFC 8032 Ed25519 signed KILL_PROCESS or SIGCONT verified against (PID, process_start_time_ns).
02 · Sensor Footprint & OS Compatibility

Kernel-Safe Rust eBPF & Windows ETW Specifications

  • Linux Endpoint Sensor Kernel 5.4+ BTF CO-RE (Ubuntu, Debian, RHEL, Alma, Rocky, Amazon Linux) · <1.2% median CPU · <42 MB RSS RAM.
  • Windows Endpoint Sensor Windows Server 2019, 2022, 2025 & Windows 10/11 Enterprise via native kernel/user ETW providers & AMSI.
  • Critical PID Guardrail Hardcoded exclusion prevents suspension of core OS & database daemons (systemd, sshd, postgres, lsass.exe).
  • Offline Resilience Continues local L0/Tier-0 protection with bounded ring-buffer disk spooling if control-plane connectivity drops.
03 · AI Model Card & Fine-Tuning Provenance

Sovereign-Hosted, Domain-Fine-Tuned 33B & 50B Models

Our 5-Agent SOC Swarm executes on open-weight foundation architectures domain-fine-tuned via QLoRA/SFT on curated MITRE ATT&CK v15 syscall graphs, Linux auditd/eBPF traces, Windows ETW Event IDs, and obfuscated PowerShell/Bash/PHP exploit corpora.

Adversarial Prompt-Injection Defense: Command-line arguments are sanitized and deobfuscated before inference, and agent outputs are strictly constrained to deterministic JSON verdict schemas—preventing arbitrary command execution. Hosted in our India Sovereign Pod, Australia & New Zealand On-Shore Sovereign Pod, or customer air-gapped GPU appliances.

04 · Regulatory Alignment vs. Formal Certification

Transparent Enterprise Compliance Taxonomy

Implemented Security Controls: TLS 1.3 transport, AES-256/Fernet encryption at rest, RFC 8032 Ed25519 command signing, and NIST FIPS 203/204 PQC CBOM auditing.

Regulatory Control Alignment: Provides automated technical controls (NIC/NPL NTP sync check, 180-day tamper-evident log retention on Corporate+ or via S3 archival on Starter–Growth, and 6-hour/72-hour incident dossiers) mapped to CERT-In Directions (28.04.2022), DPDP Act 2023, ACSC Essential Eight, APRA CPS 234, SOCI Act, ISO/IEC 27001:2022 Annex A, and SOC 2 Type II control criteria.

05 · Reproducible Benchmark Verification & 60-Second Deployment

Validate All 5 Tiers in Your Own Linux & Windows Environment

Every latency and detection benchmark published on nikada.in—from 0.051 ms P50 L0 filtering and 0.131 ms P50 Tier-0 process micro-freeze to 14.35 ms P50 BETH eBPF DualEngine ML (99.74% accuracy) and 0.054 ms P50 Ed25519 command signing—can be independently reproduced in your staging or production fleet in under 60 seconds.

Inspect Full Evidence Library → Request 60-Second Deployment →